

Vulnerability Findings Cron
Retrieves vulnerability data and associated metadata for assets from Crowdstrike Falcon Spotlight, including details like CVE identifiers, CVSS scores, descriptions, solution information, and affected systems.
Sync Type: Full Synchronization
Requirements
- Before you connect Monad to CrowdStrike, you need a Client ID and Client Secret. Log in to your CrowdStrike portal, and under Support & Resources, click on 'API Client and Keys' to create your credentials.
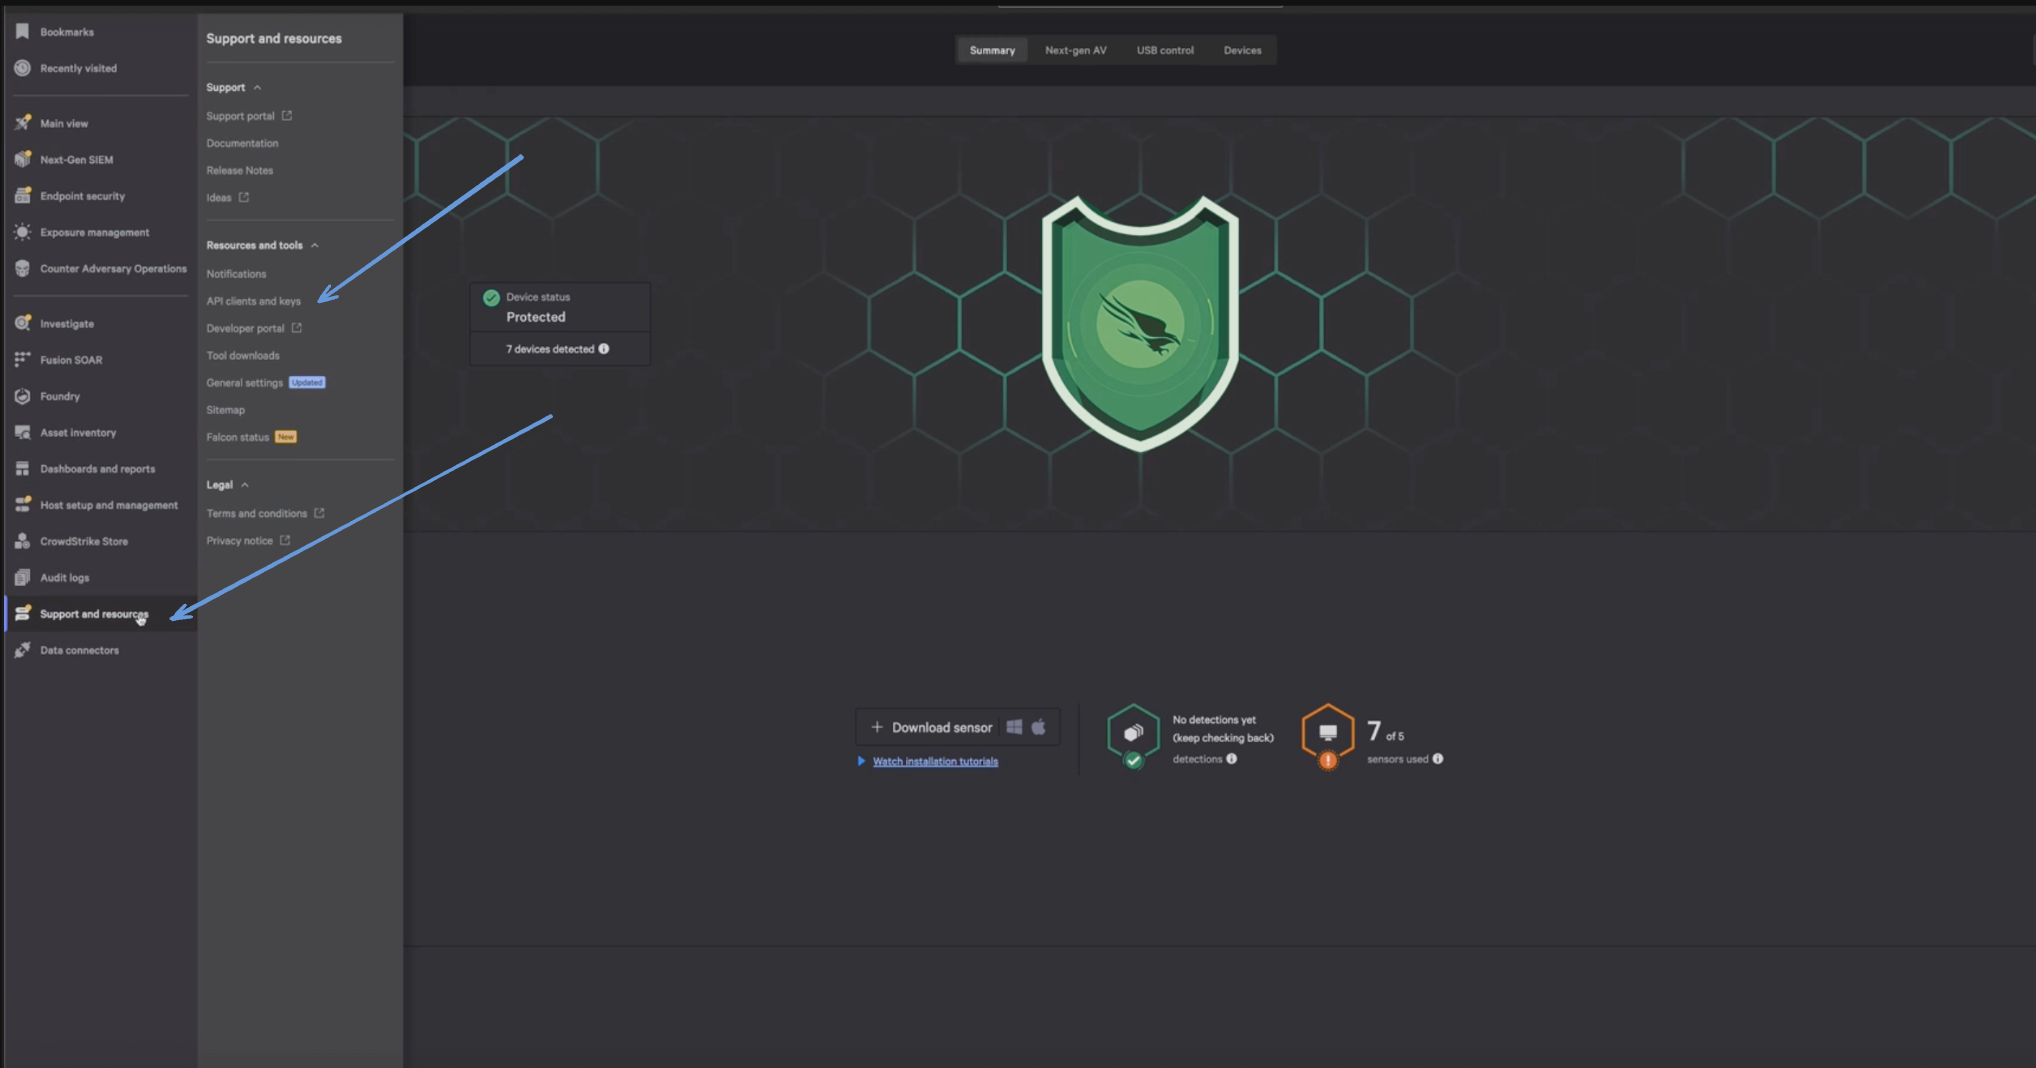
- Enter a Client Name, Description and API Scopes to define the API client. Ensure read roles for User Management are enabled.
- Click Done.
- Copy the ClientID and ClientSecret key. You'll need them when you set up the Monad connector.
Details
The same vulnerabilities from crowdstrike-vulnerabilities are returned but a full sync is performed based on a set cron schedule.
Configuration
The following configuration defines the input parameters. Each field's specifications, such as type, requirements, and descriptions, are detailed below.
Settings
| Setting | Type | Required | Description |
|---|---|---|---|
| Cron | string | Yes | Cron string for scheduling tasks. Ex: '0 0 * * *' for daily execution at midnight. |
| Cloud Type | string | No | Your cloud type for CrowdStrike. Ex: 'autodiscover', 'us-1', 'us-2', 'eu-1', 'us-gov-1'. |
Secrets
| Secret | Type | Required | Description |
|---|---|---|---|
| Client ID | string | Yes | Client ID for the CrowdStrike API. This is required to authenticate requests. |
| Client Secret | string | Yes | Client Secret for the CrowdStrike API. This is required to authenticate requests. |
OCSF Conversion
The following JQ transformation converts Crowdstrike Vulnerability data to OCSF Version 1.1 compliant format.
Sync frequency
This input runs on a cron schedule (default hourly, 0 * * * *), which you can configure on the pipeline. See Input Sync Frequency for details.