Retrieves vulnerability data and associated metadata for assets from Tenable, including details like CVE identifiers, CVSS scores, descriptions, solution information, and affected systems.
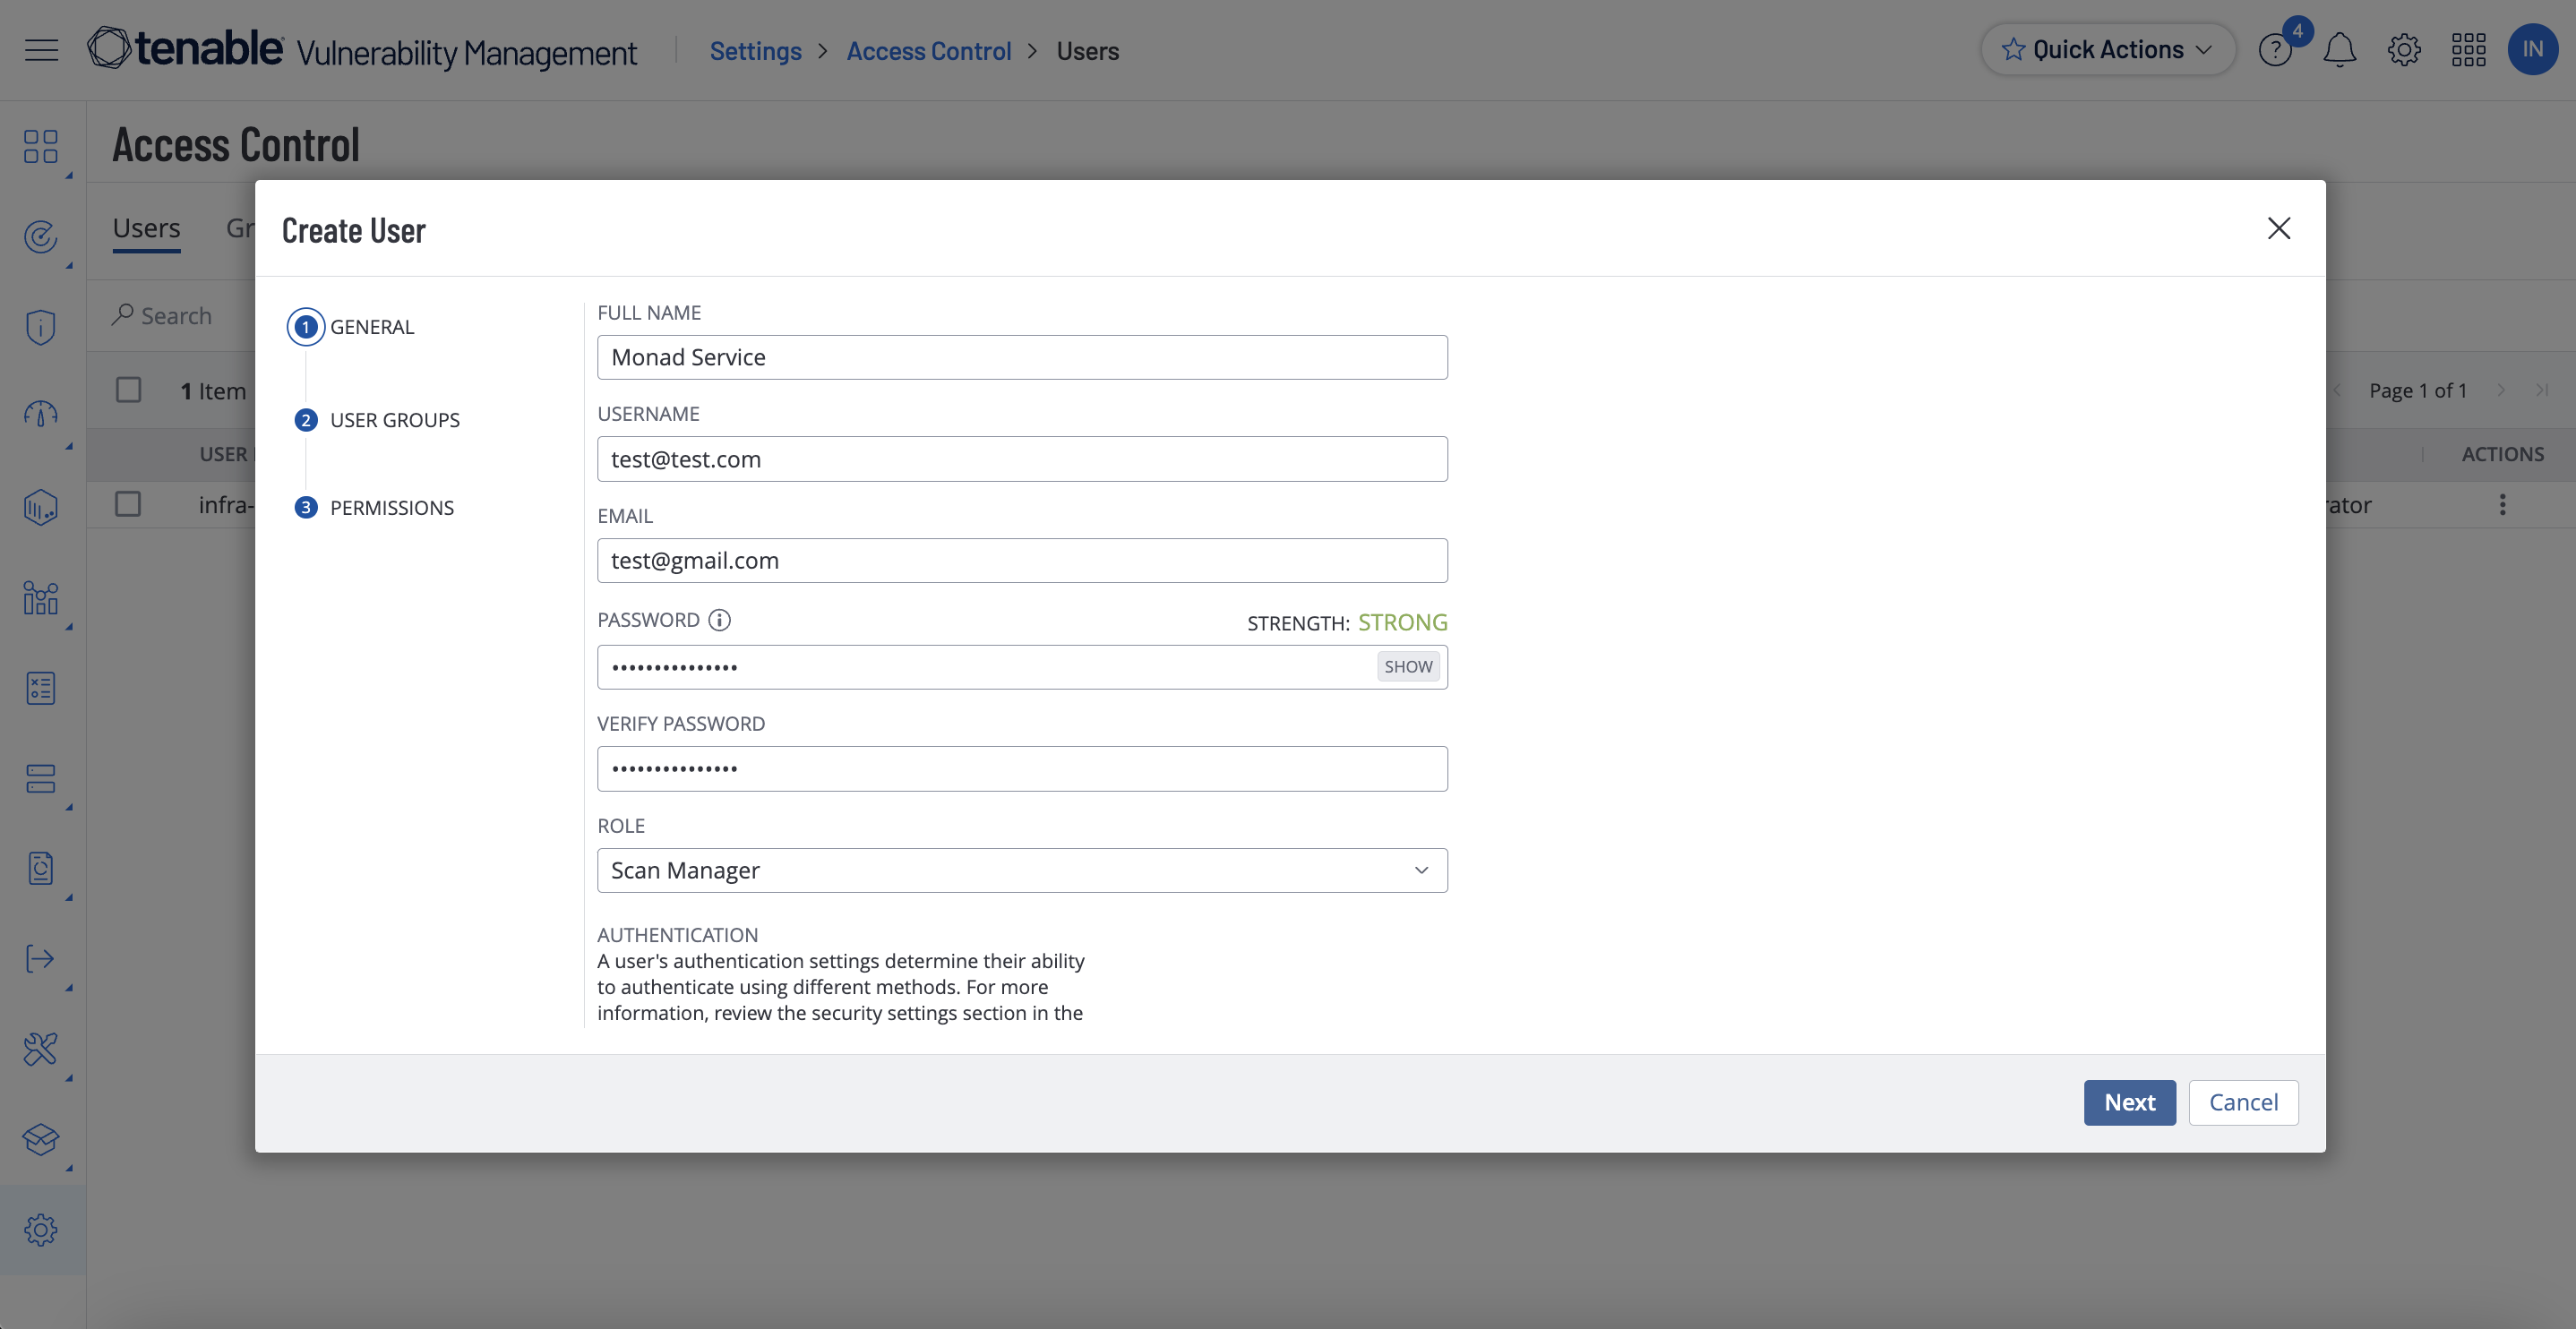
Fill out the rest of the service account fields using your organization's usual process.
Set the Role to Scan Manager and click Finish.
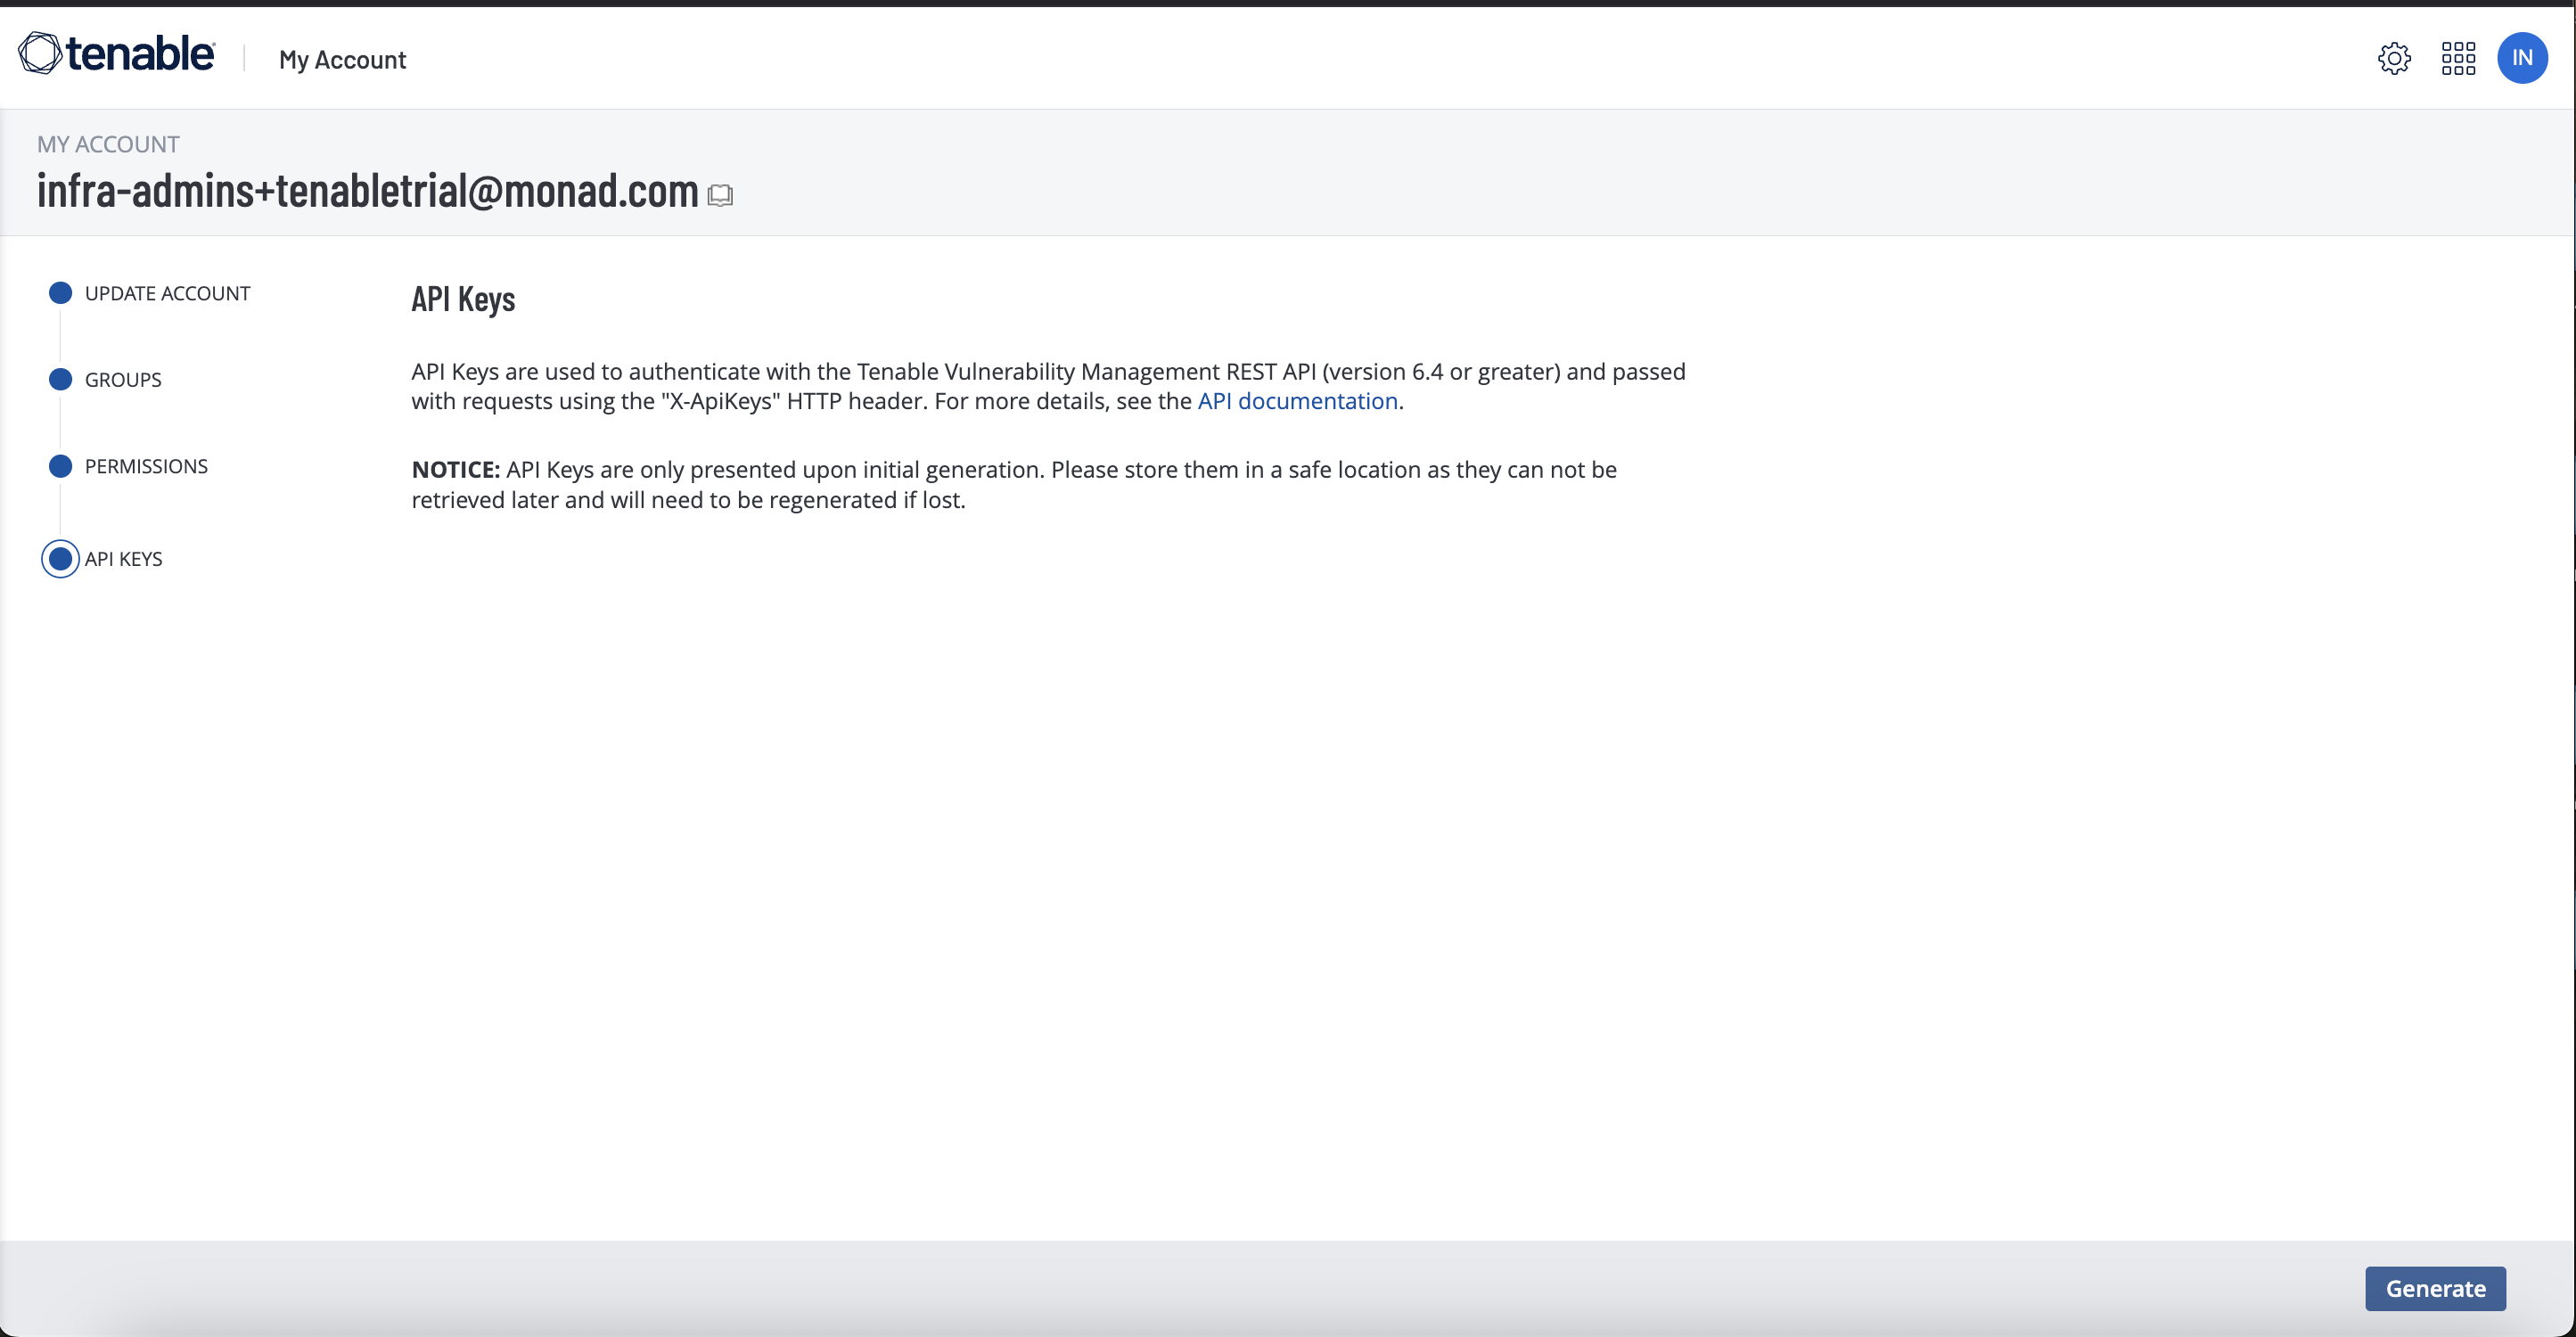
Click the new service user and select API Keys on the left.
Copy the access key and secret key. You'll need them when you set up the Monad connector.
Details
Monad exports vulnerabilities using the since and state filters on the Tenable API. The since value is the watermark from the previous successful run, so each run only fetches what changed.
since is qualified differently depending on a vulnerability's state:
OPEN and REOPENED records are matched on when they were last found.
FIXED records are matched on when they were last fixed.
By default Monad requests OPEN and REOPENED only, which matches Tenable's own behavior when the filter is omitted. Remediations are therefore not collected unless you ask for them.
To capture remediations, add FIXED to Vulnerability States. A vulnerability that was open for months and fixed yesterday has a last_found date well before the current watermark but a last_fixed date after it, so Monad compares each record against whichever of the two is later. Expect a one-time increase in record volume after enabling it.
Note that Tenable's export only reflects changes to a vulnerability's state. Edits to other fields on an otherwise unchanged vulnerability do not move last_found or last_fixed, so they will not appear in an incremental export.
Configuration
The following configuration defines the input parameters. Each field's specifications, such as type, requirements, and descriptions, are detailed below.
Settings
Setting
Type
Required
Description
Backfill Start Time
string
No
The date to start fetching data from. If not specified, no past records will be fetched.
Vulnerability States
array of string
No
Vulnerability states to fetch: OPEN, REOPENED, FIXED. Defaults to OPEN and REOPENED. Add FIXED to also collect remediations.
API Rate Limit
object
No
Optional limit on the connector's outbound request rate to the source API. Leave blank to use the connector's default behavior. See API Rate Limiting for the field format, limits, and how to choose a value.
Secrets
Secret
Type
Required
Description
Access Key
string
Yes
Access Key for the Tenable API. This is required to authenticate requests.
Secret Key
string
Yes
Secret Key for the Tenable API. This is required to authenticate requests.
OCSF Conversion
The following JQ transformation converts Tenable Vulnerability data to OCSF Version 1.0.0-rc.2 compliant format.
By default this input polls approximately every 10 seconds, with each sync beginning after the previous one completes. A cron schedule configured on the pipeline overrides this cadence. See Input Sync Frequency for details.